AI Voice Fraud Needs Three Seconds of Your Voice
TL;DR
AI voice fraud needs only three seconds of audio to clone a voice, and detection has failed. The defenses that work and what voice tech builders should change.
Last updated: July 15, 2026
A recent article from SmarterArticles breaks down why AI-powered voice fraud has become a mainstream criminal tool - and why the standard "detect the fake" approach has fundamentally failed. The piece hit the Hacker News front page and sparked a discussion that's worth unpacking for anyone building voice tech, authentication systems, or just wondering whether they should answer the phone anymore.
The Three-Second Reality#
The core technical claim: a fraudster needs only three seconds of audio to create a convincing synthetic voice. That's not a theoretical capability - it's deployed infrastructure. The article cites $893 million in AI-enabled fraud losses reported to the FBI in 2025, with $352 million of that coming from victims aged 60 and older.
The opening case study describes Sharon Brightwell, a Florida retiree who lost $15,000 after receiving a call from what sounded exactly like her daughter claiming to need bail money. The voice was synthetic. She only discovered the deception after calling her actual daughter.
This isn't new as a scam pattern - "grandparent scams" have existed for decades. What's new is the fidelity. The caller doesn't need to sound vaguely like a panicked relative. They sound exactly like that relative.
Detection Has Failed#
The most technically significant admission in the article comes from Hany Farid, UC Berkeley's leading deepfake forensics expert. According to the article, Farid admitted he can no longer reliably distinguish authentic recordings from synthetic ones.
This undermines the entire premise that technology can outpace fraudulent generation. If the world's top forensics researcher can't tell the difference, neither can automated detection systems, and certainly not the elderly targets of these scams.
The article frames this as a categorical failure of the detection paradigm, not a temporary gap that better AI will close. The generators improve faster than the detectors.
What HN Is Saying#
The Hacker News discussion surfaced several practical responses that go beyond the article's recommendations.
"Okay, let me call you right back." Multiple commenters pointed to this as the simplest defense - if someone claims to be calling from jail or a borrowed phone, hang up and dial the person directly. The scam depends on maintaining the fiction across a single call.
Family safe words. Several people mentioned establishing authentication phrases known only to family members. "Tell me something only we know" becomes a verification protocol.
The phone-as-liability problem. One commenter noted the recursive trap: "So, you answer your phone to the scam and... now they have your voice too." Every phone conversation potentially supplies material for future attacks.
Banks pushing voice ID. Several commenters expressed frustration that banks continue to push voice authentication as a security feature, even as voice cloning makes that authentication trivially bypassable. "Did ya'll never play Uplink?" one asked.
The KYC futility argument. At least one commenter argued the problem is fundamentally unsolvable: "Once a model exists it's trivial to spread it around, and for organized groups to get ahold of those." No amount of regulation limits the actual criminal use once the capability exists.
The Article's Four Recommendations#
The article proposes structural approaches rather than technical ones:
-
Abandon detection as primary defense. Stop pretending we can reliably tell real from fake. Build systems that don't depend on that distinction.
-
Regulate voice-cloning supply. Mandate verifiable consent before cloning voices, similar to Tennessee's ELVIS Act. This limits casual misuse but does little against organized crime. Some vendors now sidestep cloning entirely: OpenAI prompt-to-voice builds a new voice from a written description with no recording, and bans imitation of named people.
-
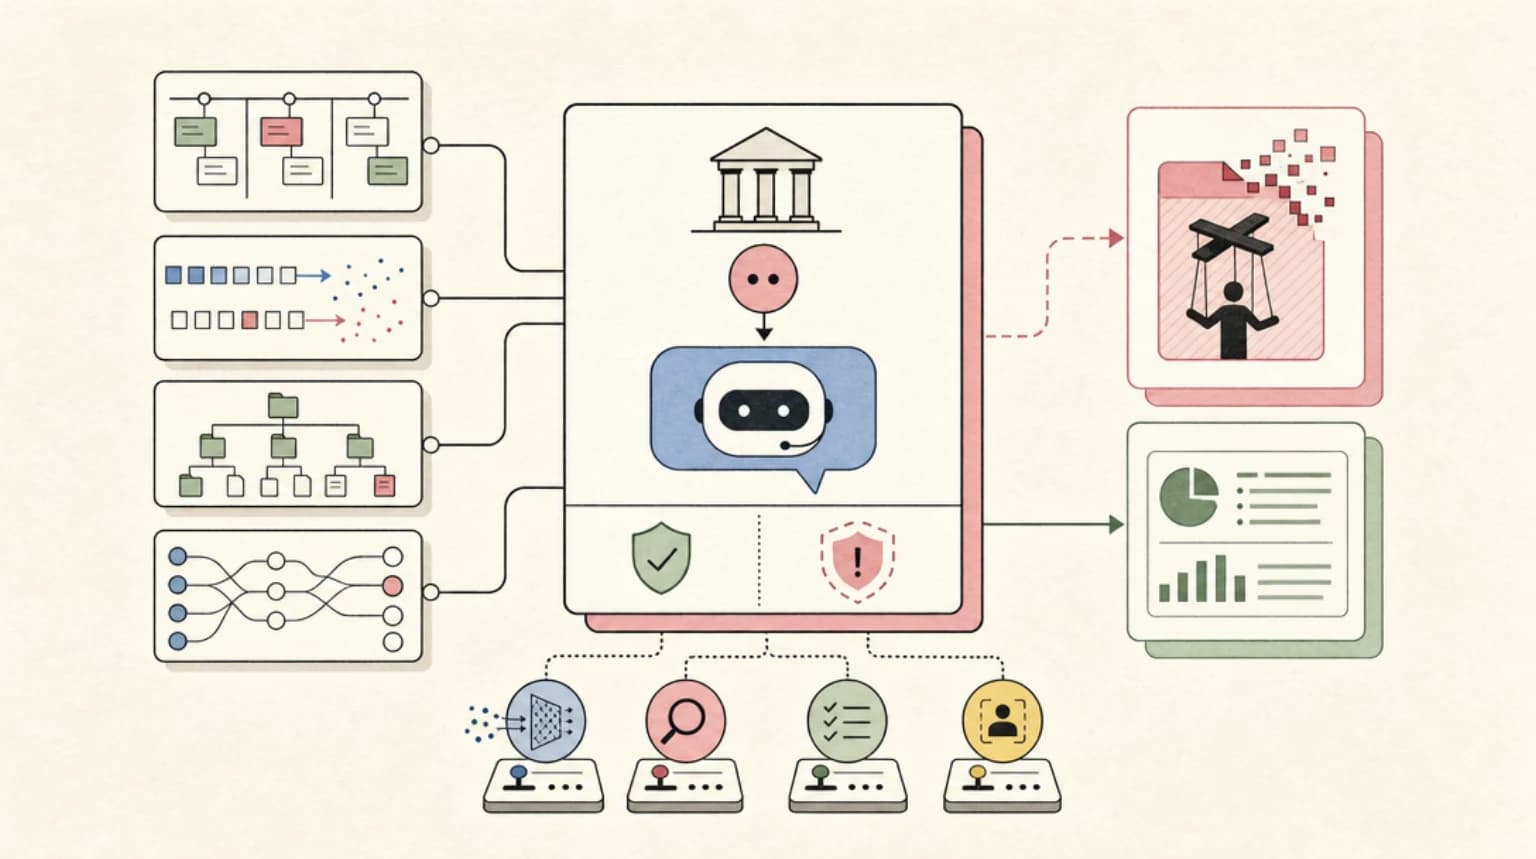
Place responsibility on institutions. Shift liability from vulnerable individuals to banks, telecom carriers, and platform providers. The UK's reimbursement mandate for authorized push payment fraud is cited as a model - when banks pay for fraud, they suddenly find ways to prevent it.
-
Manage human vulnerability systematically. Treat cognitive and emotional exploitation like software vulnerabilities - something to be cataloged, studied, and mitigated at the systems level rather than blamed on individual victims.
The institutional liability angle is the most actionable for developers. If your system processes voice for authentication or identity, the regulatory environment is shifting toward holding you responsible when that authentication gets bypassed.
What Developers Should Know#
If you're building anything that touches voice:
Voice-only authentication is deprecated. Treat it as a weak signal at best, not a security boundary. Combine it with other factors or replace it entirely.
Synthetic detection APIs exist but shouldn't be trusted. The article's point about forensics experts failing applies to commercial detection services too. They're useful for flagging low-quality fakes but won't catch state-of-the-art synthesis.
Your users' voice samples are sensitive data. Three seconds is enough. Customer service recordings, voicemails, and any audio you retain can be weaponized. Apply the same data minimization principles you'd apply to passwords.
The regulatory direction is toward liability. Build audit trails now. When regulators ask how fraud happened through your system, "we couldn't detect the fake" won't be an acceptable answer.
The HN discussion is worth reading for the practical defenses people have implemented in their own families - the "call back" protocol, safe words, and general paranoia about urgent requests for money are all low-tech mitigations that actually work.
The broader question - whether we want to live in a world where phone calls are fundamentally untrustworthy - is one the article doesn't answer. But for builders, the immediate takeaway is clear: assume voice can be faked, and design accordingly.
FAQ#
How much audio does AI voice cloning need?#
According to the SmarterArticles piece, a fraudster needs only three seconds of audio to create a convincing synthetic voice. That is why customer service recordings, voicemails, and any retained audio should be treated as sensitive data.
Can AI voice deepfakes be reliably detected?#
Not reliably. The article reports that Hany Farid, UC Berkeley's leading deepfake forensics expert, can no longer reliably distinguish authentic recordings from synthetic ones. Commercial detection services may flag low-quality fakes but should not be trusted to catch state-of-the-art synthesis.
How can families protect themselves from AI voice scams?#
The practical defenses raised in the HN discussion are low-tech: hang up and call the person back on a number you know, and agree on a family safe word or a question only family members can answer. The scam depends on keeping the fiction going across a single call.
Is voice authentication still safe for banks and apps?#
Voice-only authentication should be treated as a weak signal at best, not a security boundary. Combine it with other factors or replace it entirely, and build audit trails, since the regulatory direction is toward holding institutions liable when authentication is bypassed.
Continue Reading#
- OpenAI Open-Sourced Codex Security: What HN Thinks
- Codex Security Preview: AppSec Agent for Real Repos
- Cursor 0day: Why a 7-Month-Old Vulnerability Is Still Unpatched
Sources#
- The Three-Second Theft: Why AI Voice Fraud Outruns Every Defence - SmarterArticles
- Hacker News Discussion - 132 comments
Get the next deep dive like this in your inbox
One email a week on News and the rest of the AI dev stack. Free.
Read next
Ghost Font: Text That Humans Can Read But AI Cannot
Ghost Font hides text in video using motion, so humans can read it but frame-by-frame AI models cannot. How it works and how HN commenters broke it.
6 min readGLM 5.2 Outperforms Claude Code on Semgrep's IDOR Vulnerability Benchmarks
GLM 5.2 vs Claude Code on Semgrep IDOR benchmarks: the open-weight model scored higher at about one-sixth the cost per finding. Setup, results and HN reactions.
6 min readVulnerability Reports Are Not Special Anymore
Filippo Valsorda argues LLMs have made vulnerability reports less special. His case against old coordinated disclosure norms, plus the HN pushback.
7 min readNew here? Start with
Technical content at the intersection of AI and development. Building with AI agents, Claude Code, and modern dev tools - then showing you exactly how it works.